Embed script
before.js opens the Before sale wizard in a modal over your page. It has no dependencies and works with any framework.
<script src="https://app.before.com/embed/v1/before.js"></script>
The v1 path stays backward compatible; breaking changes get a new path. The
file is small and cached for five minutes, so fixes reach you without a
release on your side.
Before.open(options)
const handle = Before.open({
  token: session.session_token,
  onComplete: ({ sale_id, status }) => {
    // The sale went out for signature, was signed or was submitted.
  },
  onExit: ({ reason }) => {
    // 'closed': the user closed the wizard. 'expired': the session ran out.
  },
});

// Later, to take the modal down yourself:
handle.close();
| Option | Meaning |
|---|---|
token | Required. The session_token from POST /v1/partner/sessions. |
onComplete | Called once per open, on the first move into out_for_signature, signed or submitted while the modal is open. It receives sale_id and status. A sale that was already past that point when opened does not call it. |
onExit | Called after the modal is removed, with reason closed or expired. |
baseUrl | Optional. The Before app to open; leave it unset. |
open returns { close }. close() removes the modal and does not call
onExit.
onComplete is a convenience for your interface, such as closing the modal or
marking the case sold. Treat webhooks or
GET /v1/partner/sales/:id as the record of what happened.
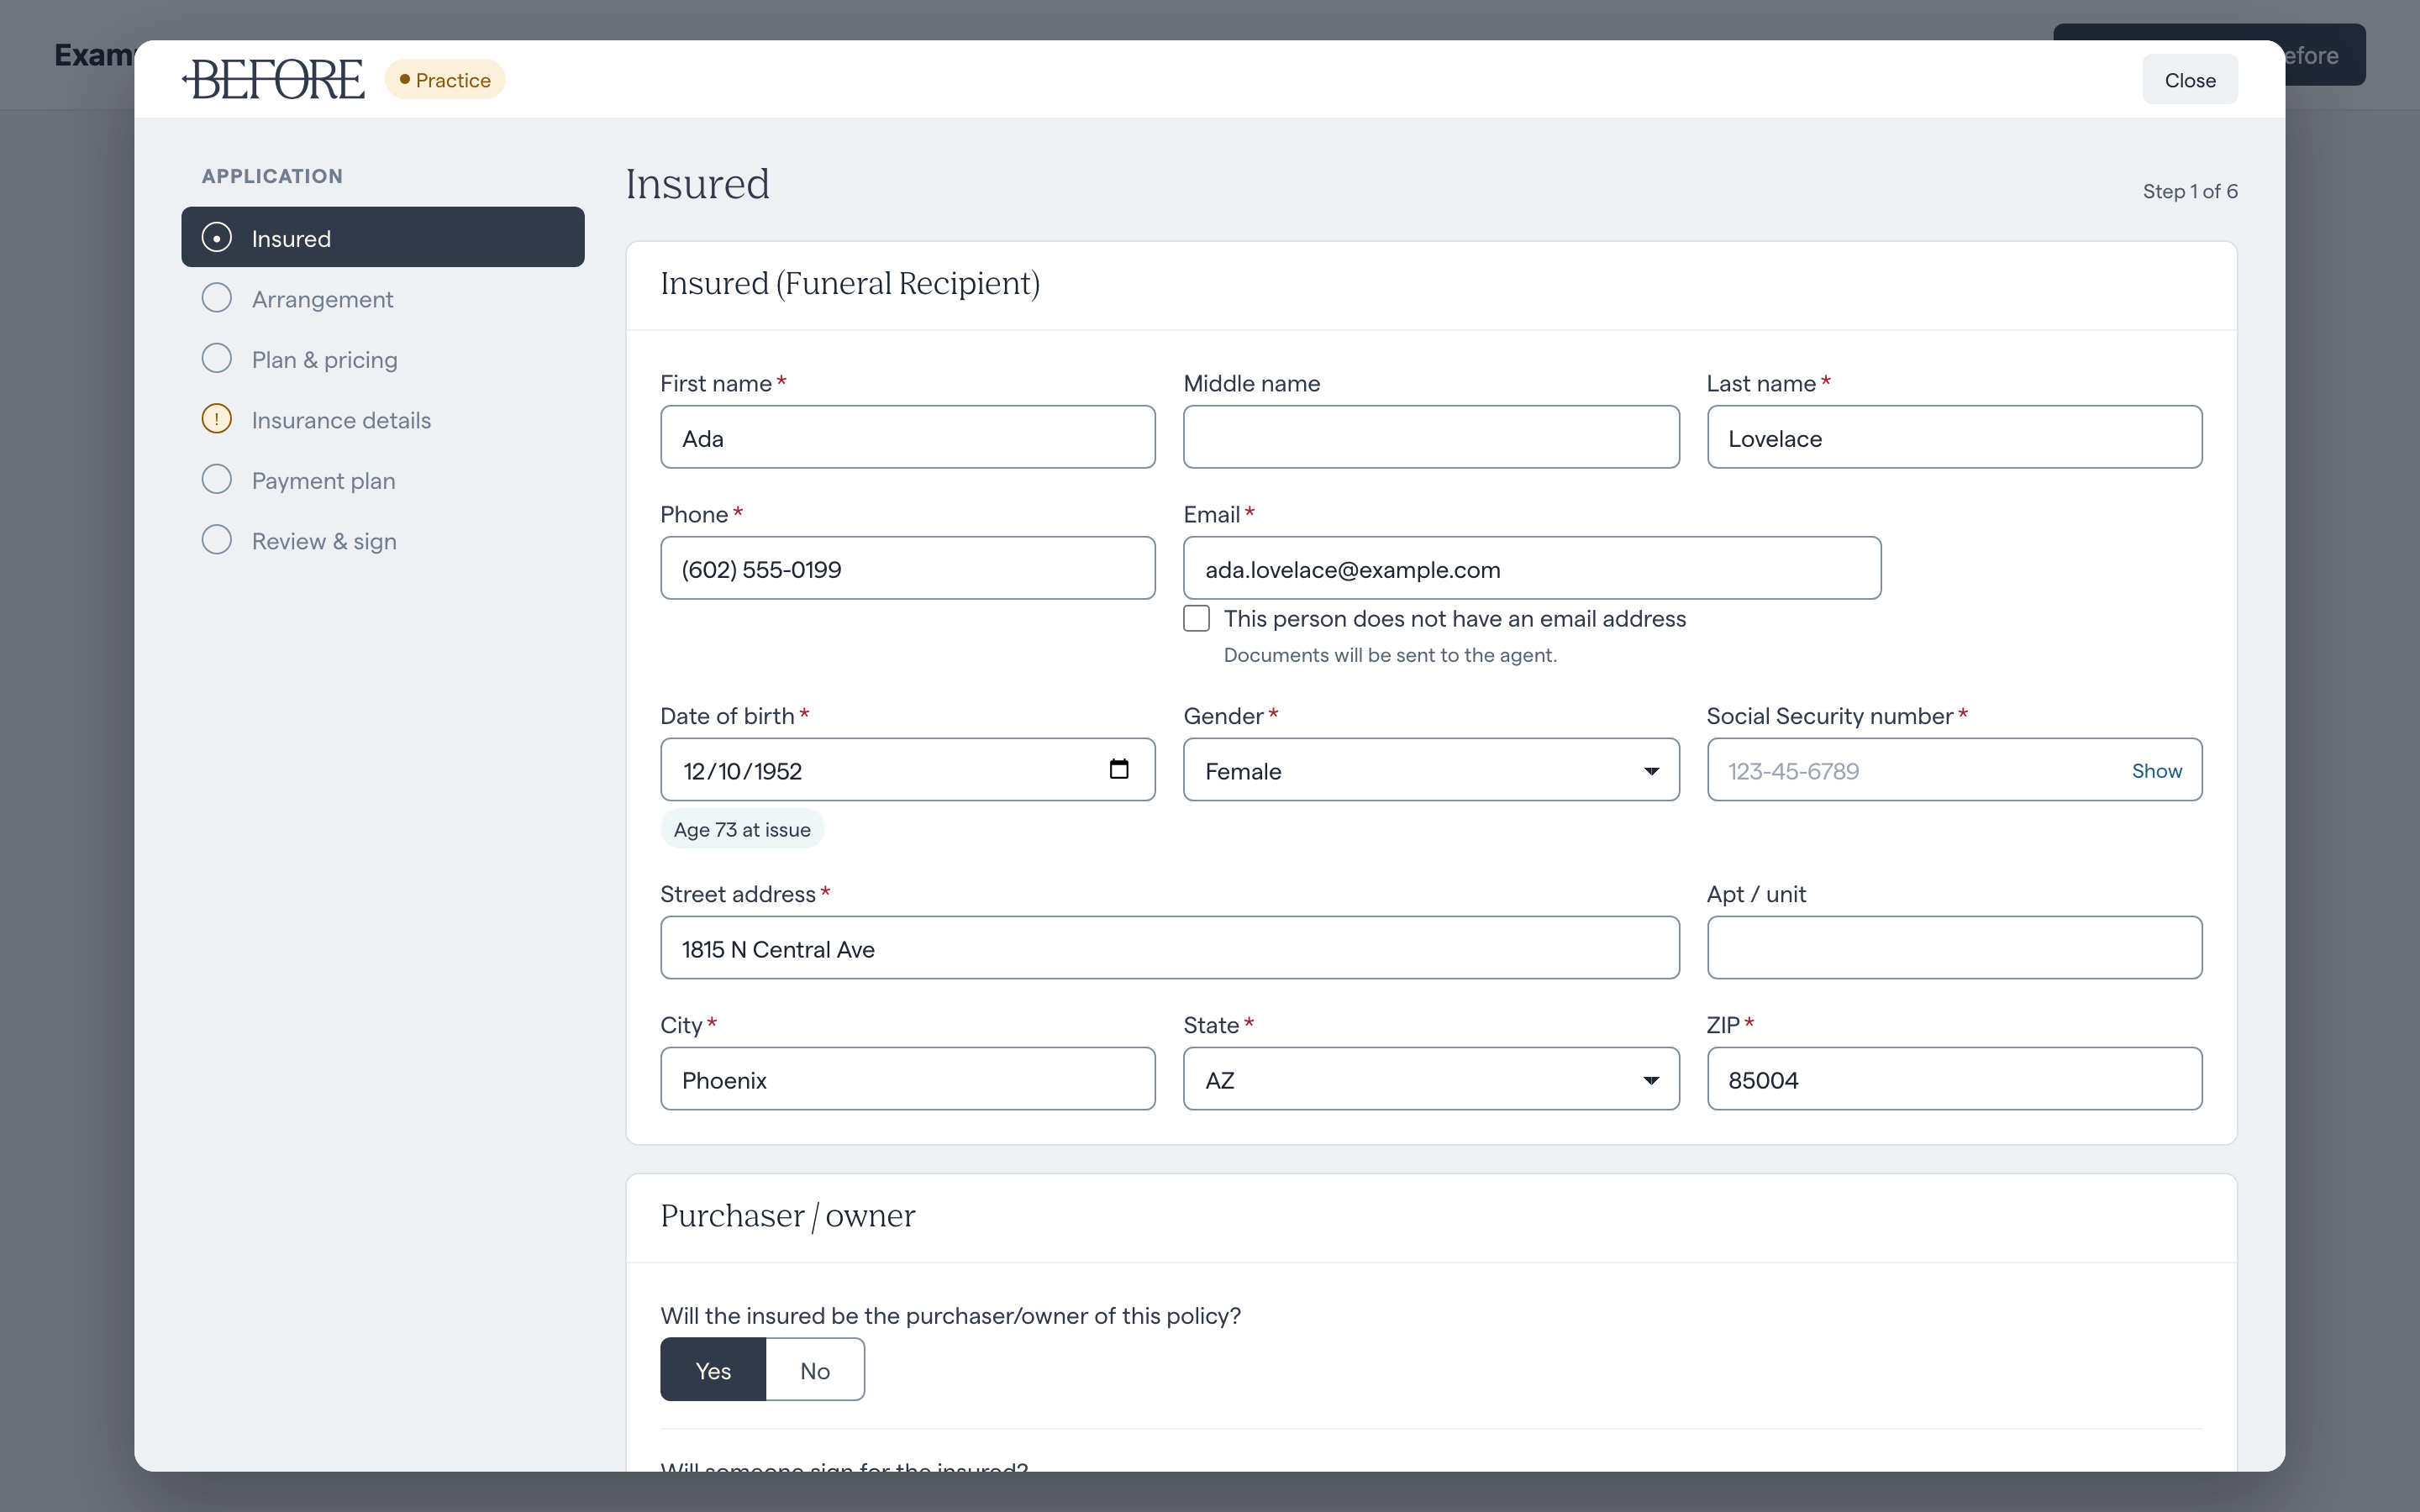
A session created with a test key shows a Practice pill in the modal header.
The user needs no Before sign-in inside the modal: the session token is their credential for this one sale, and it lives only in the modal's memory, so the wizard does not depend on third-party cookies.
Allow your page to frame the wizard
The browser and before.js each check origins before anything reaches your
page.
Two lists must name the origin of every page that calls Before.open, for
example https://crm.example.com:
- The API key's embed origins, which you edit in the Before Partner Portal. The wizard posts its events only to these origins.
- Before's framing allowlist. The browser refuses to show the wizard in a page Before has not allowed. Before adds every origin you register, and it takes effect with Before's next deploy, usually within a business day.
Both take HTTPS origins only. While you develop, use an HTTPS tunnel to your machine and register its origin.
If your page sends a Content Security Policy, allow the script and the frame:
script-src https://app.before.com;
frame-src https://app.before.com;
Session expiry
A session token lasts two hours and is never refreshed. Once it has run out,
the wizard's next call to Before fails, the modal closes and onExit receives
expired. Open a new
session with the same partner_reference to carry on; nothing the user
entered is lost.
A token that has already expired when the wizard loads cannot report back: the
wizard shows an expiry notice and your page hears nothing. Open sessions just
before calling Before.open, rather than ahead of time, and close the modal
yourself once expires_at has passed.
Security
- The script acts only on messages from the Before app's origin and from its own frame; it ignores every other message on your page.
- The token is removed from the wizard's address bar as soon as it loads.
- Never put an API key in the page. Only the session token reaches the browser.